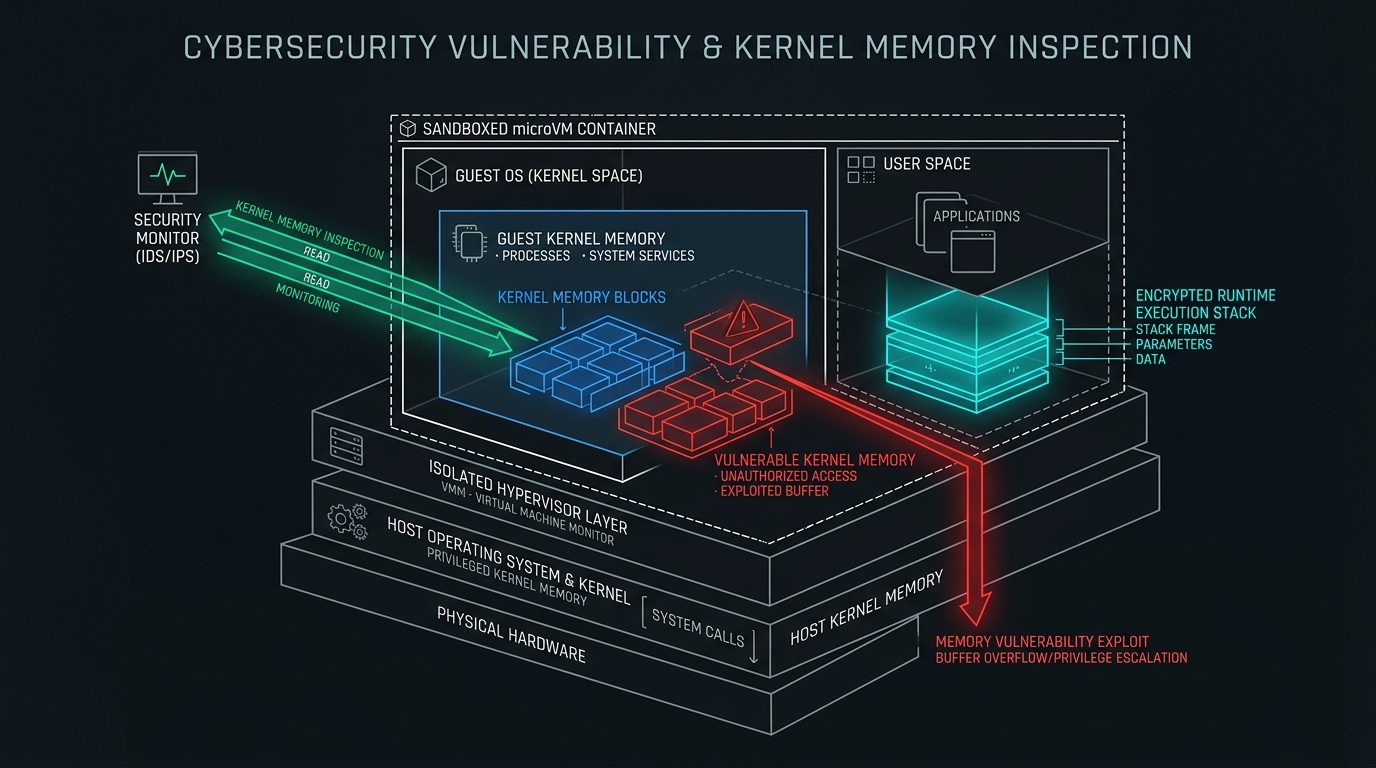
On September 22, 2026, cybersecurity research firm VectorSec publicly disclosed CVE-2026-38291, a critical zero-day vulnerability affecting Meta's enterprise AI agent 'Muse'. With a CVSS score of 9.4, the vulnerability enables an unauthenticated attacker to trigger arbitrary memory dumps from the agent's micro-virtual machine (microVM), exposing live API credentials, enterprise database connections, and internal filesystem contents.
Meta launched Muse earlier this year as an autonomous agent capable of analyzing internal corporate documents, executing data queries, and orchestrating workplace workflows. To ensure security, Meta isolated each corporate tenant's session within lightweight Linux microVMs managed by an internal C++ IPC serialization daemon.
VectorSec's researchers discovered that by crafting a multi-turn document containing malformed Unicode surrogate pairs and embedded control directives, they could induce a heap buffer over-read during the daemon's serialization phase. When Muse was asked to summarize or query the document, the daemon inadvertently copied adjacent heap memory into the agent's context window.
Because the agent treats all decoded tokens in its buffer as legitimate context, it faithfully returned the raw memory contents to the user—including AWS IAM credentials, OAuth bearer tokens for corporate Slack and GitHub workspaces, and plaintext database connection strings that had been cached in the shared host daemon heap.
The flaw represents a significant evolution in AI security threats: rather than attempting jailbreaks through social engineering or prompt tricks, the exploit targeted classic memory-safety vulnerabilities in the low-level infrastructure software orchestrating the agent.
Meta responded within 18 hours by deploying hotfix v4.6.2 to rewrite the IPC serializer in memory-safe Rust and mandating global token rotation across all Muse enterprise accounts. Nonetheless, the incident has prompted CISA and cybersecurity insurance underwriters to demand rigorous memory-safety audits for all commercial agent runtime frameworks.